ASSETUNO DIGITAL ASSET INTELLIGENCE & AUTOMATION PLATFORM
Discover everything. Understand every dependency. Automate what comes next.
AssetUno discovers software, DLLs, system components, certificates, repositories, dependencies and technology relationships across enterprise environments. It turns fragmented technical data into actionable component, license, risk and where-used intelligence, then moves from visibility to controlled automation with Auto Suite.
ONE CONNECTED PLATFORM
From fragmented technical data to actionable intelligence.
AssetUno combines discovery, intelligence and automation instead of treating them as separate operational silos. It connects technical evidence across infrastructure, applications, certificates, components and repositories so teams can understand what exists, how it is related, where it is used, what risk or license context surrounds it and what should happen next.
HOW ASSETUNO WORKS
01. Discover
Discover software, DLLs, system components, certificates, repositories and infrastructure assets.
02. Connect
Map dependencies, where-used relationships, application links and technology connections.
03. Understand
Add version, publisher, license, entitlement, vulnerability and risk context to discovered evidence.
04. Automate
Turn selected operational workflows into controlled execution with Auto Suite.
05. Ask
Use Ask AssetUno to analyze discovered technology evidence and relationships in natural language.
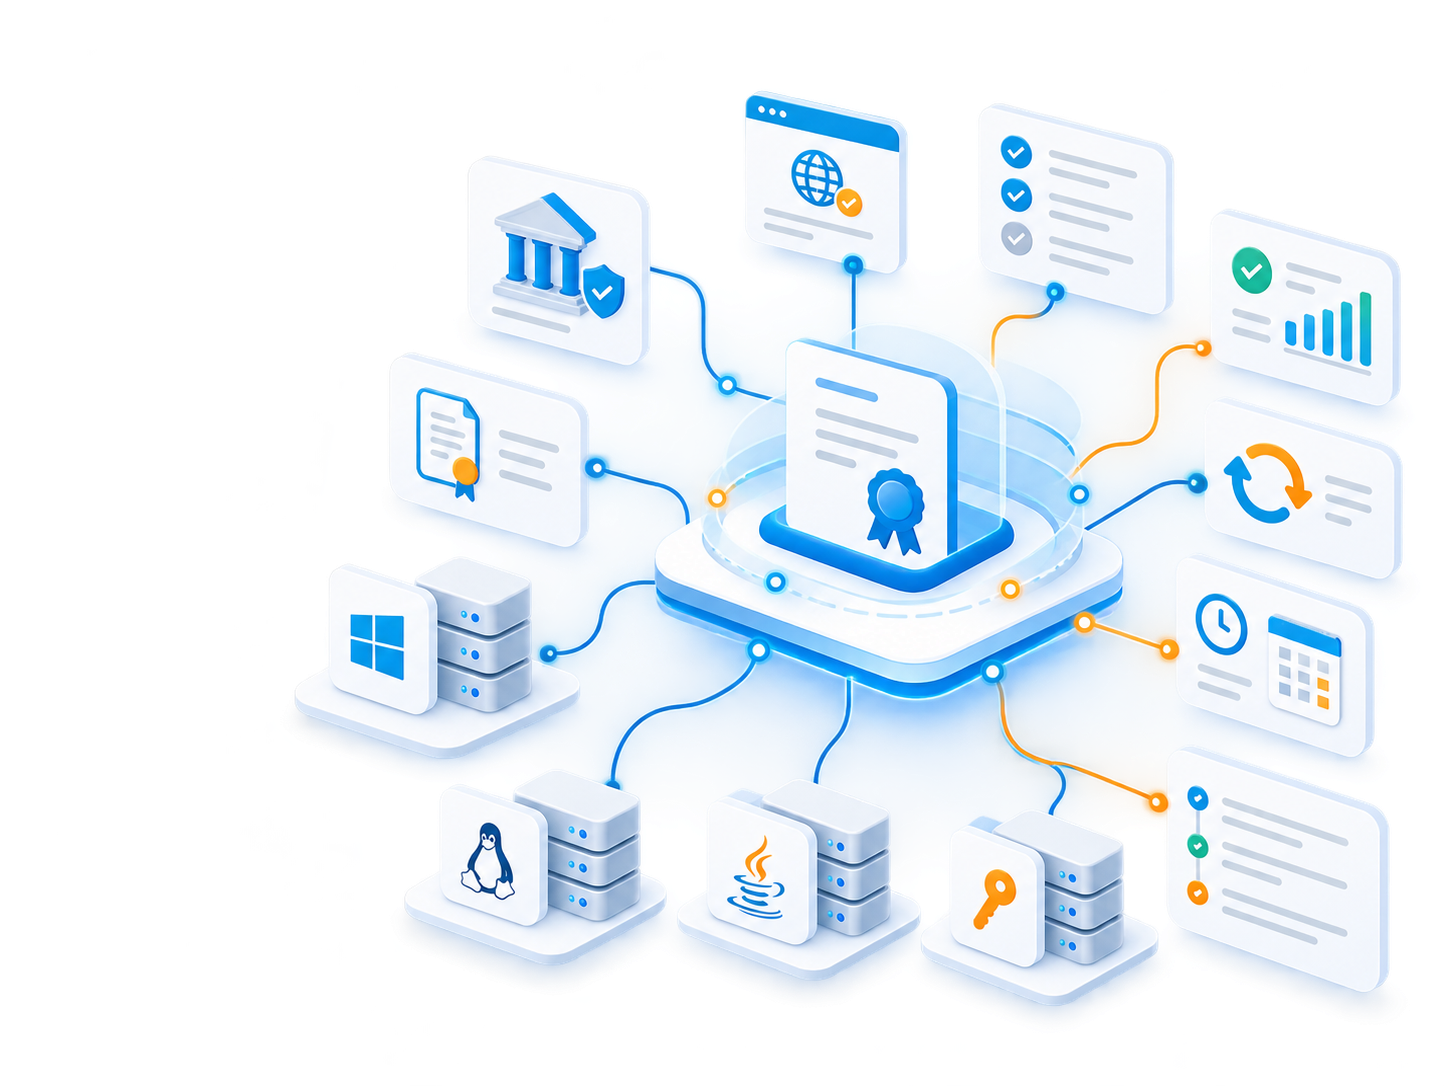
Turn Certificate Intelligence into Controlled Lifecycle Automation
AssetUno Auto Suite coordinates certificate request, validation, issuance, deployment, verification, renewal and audit in one connected enterprise workflow.
- CA provider integration and DNS validation
- Request, validation and issuance workflows
- Windows / IIS, Linux / Web, Java / JKS and PKCS12 deployment targets
- Verification, status tracking and task management
- Renewal, lifecycle history and audit evidence
Request → Validate → Issue → Deploy → Verify → Renew → Audit
Understand What Your Software Is Actually Built From
AssetUno connects binaries, DLLs, packages, dependencies, applications, hosts and artifact repositories so teams can understand what a component is, where it came from, where it is used and what risk or license context surrounds it.
- Binary and DLL evidence
- Package and dependency metadata
- Version and publisher intelligence
- Where-used relationships
- Repository reconciliation and trust context
- Risk and license context
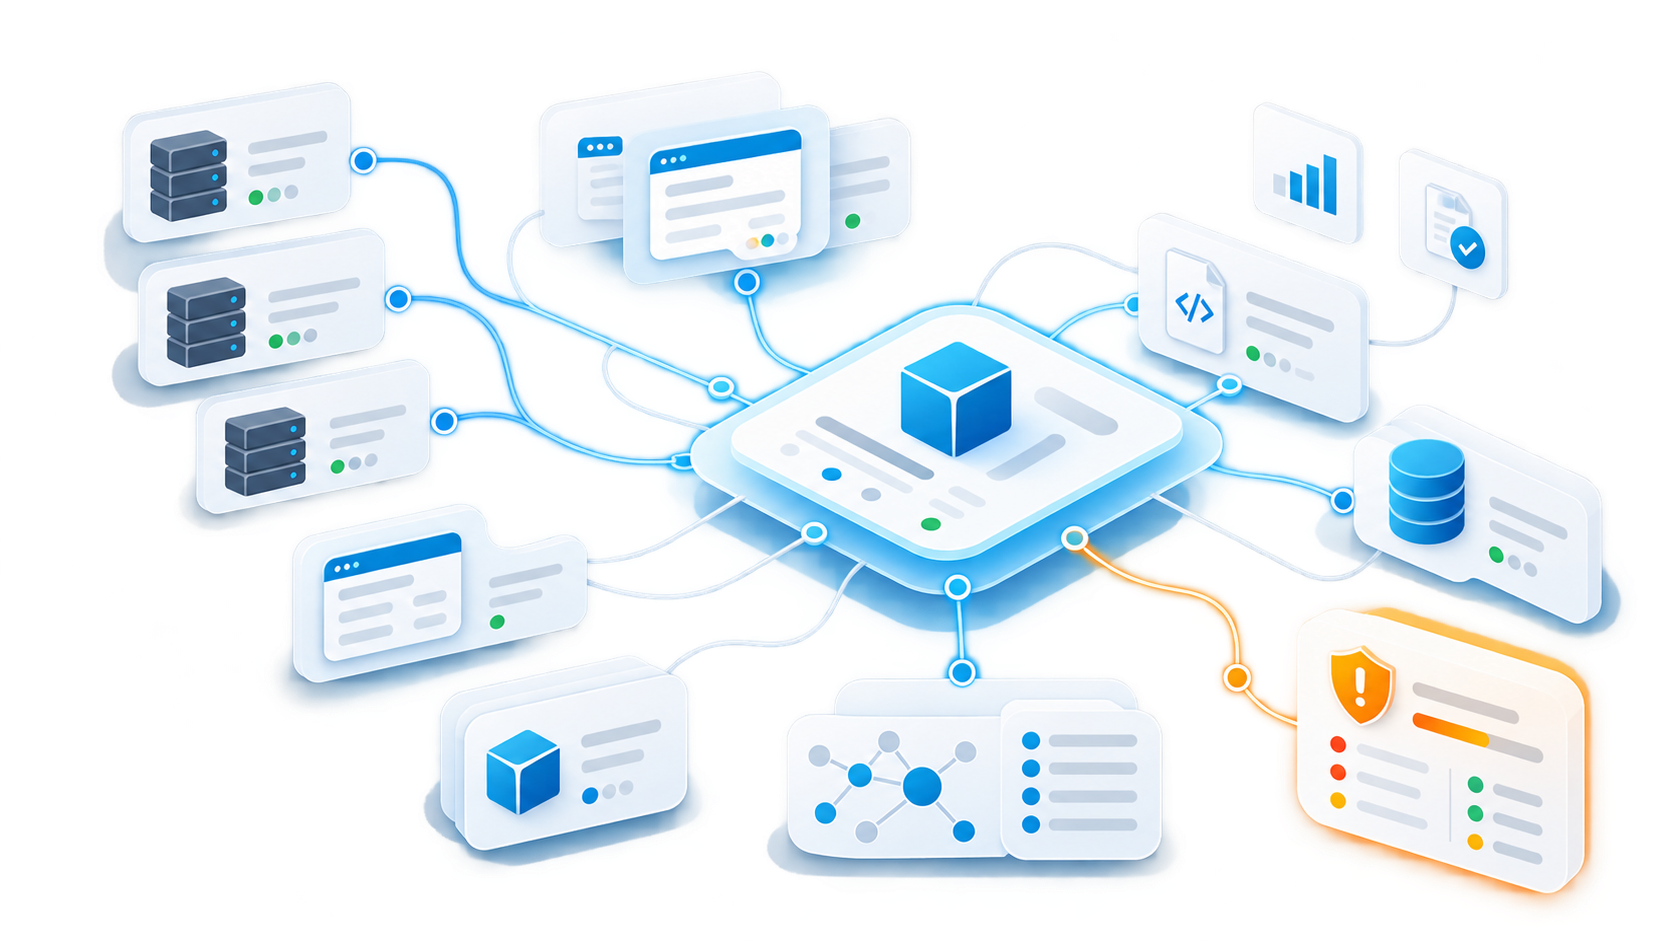
Connect Repository Packages to The Systems That Actually Use Them
AssetUno discovers repository and package evidence, reconciles it with deployed components and preserves relationships between artifact sources, versions, dependencies, applications and environments.
JFrog Artifactory
Repository and package discovery with component reconciliation, relationship context and synchronization.
Nexus Repository
Connect supported repository evidence to the shared component intelligence model.
GitHub Packages / GHCR
Bring package and registry evidence into component and dependency analysis.
GitLab Registry
Correlate supported registry evidence with deployed software context.
Harbor
Include supported artifact and registry evidence in repository intelligence.
Azure Artifacts
Connect supported Azure artifact evidence with component and dependency context.
Discover Across Network, Server, Cloud and Kubernetes Environments
AssetUno brings infrastructure targets into one discovery model and connects them with certificate, component and service evidence found around them.
- Known targets, network segments and IP ranges
- External endpoints and reachable services
- Windows and Linux / Unix systems
- Web and TLS targets
- Azure, AWS and hybrid environments
- AKS, Anthos and supported Kubernetes environments
See Certificate Exposure Before It Becomes Service Disruption
AssetUno discovers system and web certificates, identifies where they are used and keeps expiry, lifecycle, issuer and operational context connected. Auto Suite extends that visibility into controlled renewal and deployment workflows.
Discovery
Find certificate evidence across supported systems, services and web endpoints.
Where-Used
Understand which systems, services and environments depend on a certificate.
Lifecycle
Track expiry, lifecycle state, issuer and operational ownership context.
Automation Path
Move into Auto Suite renewal, deployment, verification and audit workflows.
Add Governance Context to The Technology Evidence You Discover
Technical inventory becomes more useful when teams can understand vulnerability, license, entitlement, trust, ownership and usage context around it.
Risk Intelligence
Enrich component evidence with vulnerability and CVE context, repository trust, ownership gaps and prioritization signals.
License & Entitlement
Evaluate open-source, commercial and unknown license context, conflict signals and contract or entitlement relationships where evidence is available.
Font Intelligence
Discover font family, version and publisher evidence, correlate device, application and usage context and identify commercial or unknown license exposure for review.
Ask Your Technology Environment
Ask AssetUno provides AI-assisted natural-language analysis over the technology evidence and relationships discovered by the platform. Organizations can use supported AI providers or compatible custom AI endpoints according to their architecture and governance requirements.
- Which certificates expire within the next 60 days?
- Where is this component used?
- Which applications are affected by this DLL version?
- Show components with licensing or vulnerability concerns.
- Which systems require the most urgent action?
Built to Operate Inside Enterprise Controls
Identity
Local users, LDAP, Microsoft Active Directory, Microsoft Entra ID, Okta or Keycloak, and supported OIDC/SAML configurations.
Credentials & PAM
Local credential storage plus supported CyberArk, Delinea Secret Server, BeyondTrust Password Safe, HashiCorp Vault and Generic REST secret-provider patterns.
Public API
Service accounts, controlled API tokens, external integration and API-based automation or data exchange.
Audit & Secret Protection
Audit logging, access traceability, provider test history and secret redaction. Raw secrets are not shown in normal customer views or audit records.
Start With Your Own Environment and A Focused Operational Outcome
The assessment establishes scope, connects the required sources, discovers relevant evidence, validates an automation use case and reviews the resulting findings before broader rollout.
01. Scope
Define the environment, priorities and target outcome.
02. Connect
Configure the required discovery and integration sources.
03. Discover
Collect and correlate evidence from the agreed scope.
04. Automate
Validate a controlled automation opportunity where relevant.
05. Review
Review findings, evidence and recommended next steps.
One Connected Operating Model for Technology Evidence and Action
One Inventory
Bring infrastructure, certificates, components, repositories, fonts and related evidence into a connected visibility model.
One Automation Engine
Move selected operational workflows from discovery into controlled execution, verification and lifecycle history.
One Intelligence Layer
Connect versions, dependencies, where-used relationships, vulnerability, license and entitlement context around the same evidence.
One Governance View
Give operations, security, asset management and governance teams a shared evidence base for review and action.
FREQUENTLY ASKED QUESTIONS
A few common questions.
What does AssetUno discover?
AssetUno can discover infrastructure targets, software, DLLs and system components, certificates, repository and package evidence, fonts and related technology relationships across supported enterprise environments.
What is Software Component Intelligence?
Software Component Intelligence connects binary, package, dependency, application, host and repository evidence so teams can understand what a component is, where it is used and what risk or license context surrounds it.
Can AssetUno scan artifact repositories?
Yes. AssetUno supports repository intelligence for JFrog Artifactory, Nexus Repository, GitHub Packages and GHCR, GitLab Registry, Harbor and Azure Artifacts, subject to the configured connector and permissions.
How does Auto Suite help with certificates?
Auto Suite coordinates the certificate lifecycle from request and validation through issuance, deployment, verification, renewal and audit while preserving task status and lifecycle evidence.
Can AssetUno run on-premises?
Yes. AssetUno is designed for controlled on-premises and hybrid enterprise environments, with the final architecture aligned to the required discovery scope, integrations and security requirements.
Can we use our own AI provider?
AssetUno supports supported AI providers and compatible custom AI endpoints for AI-assisted analysis, allowing organizations to align Ask AssetUno with their architecture and governance requirements.
Which languages are supported?
The AssetUno interface supports English, Türkçe, Deutsch and Italiano.
See your technology environment differently.
Discover what exists, understand how it is connected, expose the surrounding risk and license context, and automate what comes next with AssetUno.